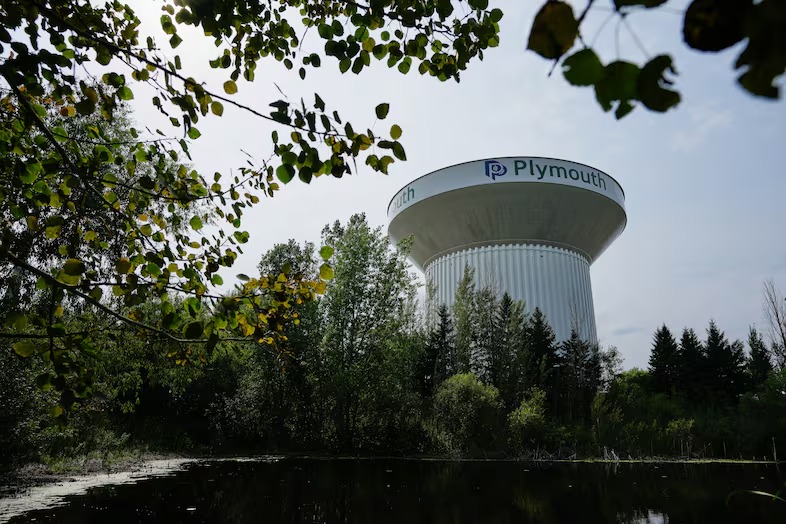
PORTLAND, OREGON — Several municipal water and wastewater utilities across Oregon have been targeted in a wave of unauthorized cyber intrusions, state officials and cybersecurity experts confirmed.
Scope of the Oregon Water System Incursions
The incidents in Oregon are part of a coordinated, multi-state cyber campaign that has targeted water treatment facilities in over a dozen states. According to the Oregon Cybersecurity Coordination Center (OC3) and federal authorities, the attacks sought to probe operational technology (OT) networks and compromise remote management systems.
Key Details of the Local Breaches
-
No Service Disruption: State regulators confirmed that water treatment plants and purification processes continued operating without interruption.
-
Drinking Water Remains Safe: Tests conducted following the intrusion verified that public water supplies across all affected Oregon municipalities remain completely safe for consumption.
-
Rapid Isolation: Utility operators detected the unauthorized network probes and quickly isolated vulnerable human-machine interfaces (HMIs) from external internet access.
Responding to Critical Infrastructure Threats
The attacks have triggered emergency briefings among state lawmakers, municipal utility leaders, and the federal Cybersecurity and Infrastructure Security Agency (CISA).
Immediate Mitigation Measures
-
Disconnecting Remote Access: Utilities across the Pacific Northwest are rushing to disable insecure remote-desktop connections and enforce mandatory multi-factor authentication (MFA) for all administrative personnel.
-
Upgrading Cybersecurity Frameworks: State agencies are deploying emergency technical assistance teams to help smaller municipal water districts patch vulnerable software and implement network segmentation.
Federal investigators continue to trace the origins of the cyberattacks, noting potential links to state-sponsored foreign threat actors targeting American critical infrastructure. Oregon water authorities have urged local utility districts to remain on high alert and report any suspicious network activity immediately.

Comment